Built for environments that can't go dark.
From day one, Innfini is engineered for regulated and federal-grade operations. Audited continuously, mapped to recognized frameworks, deployable in sovereign and air-gapped environments.
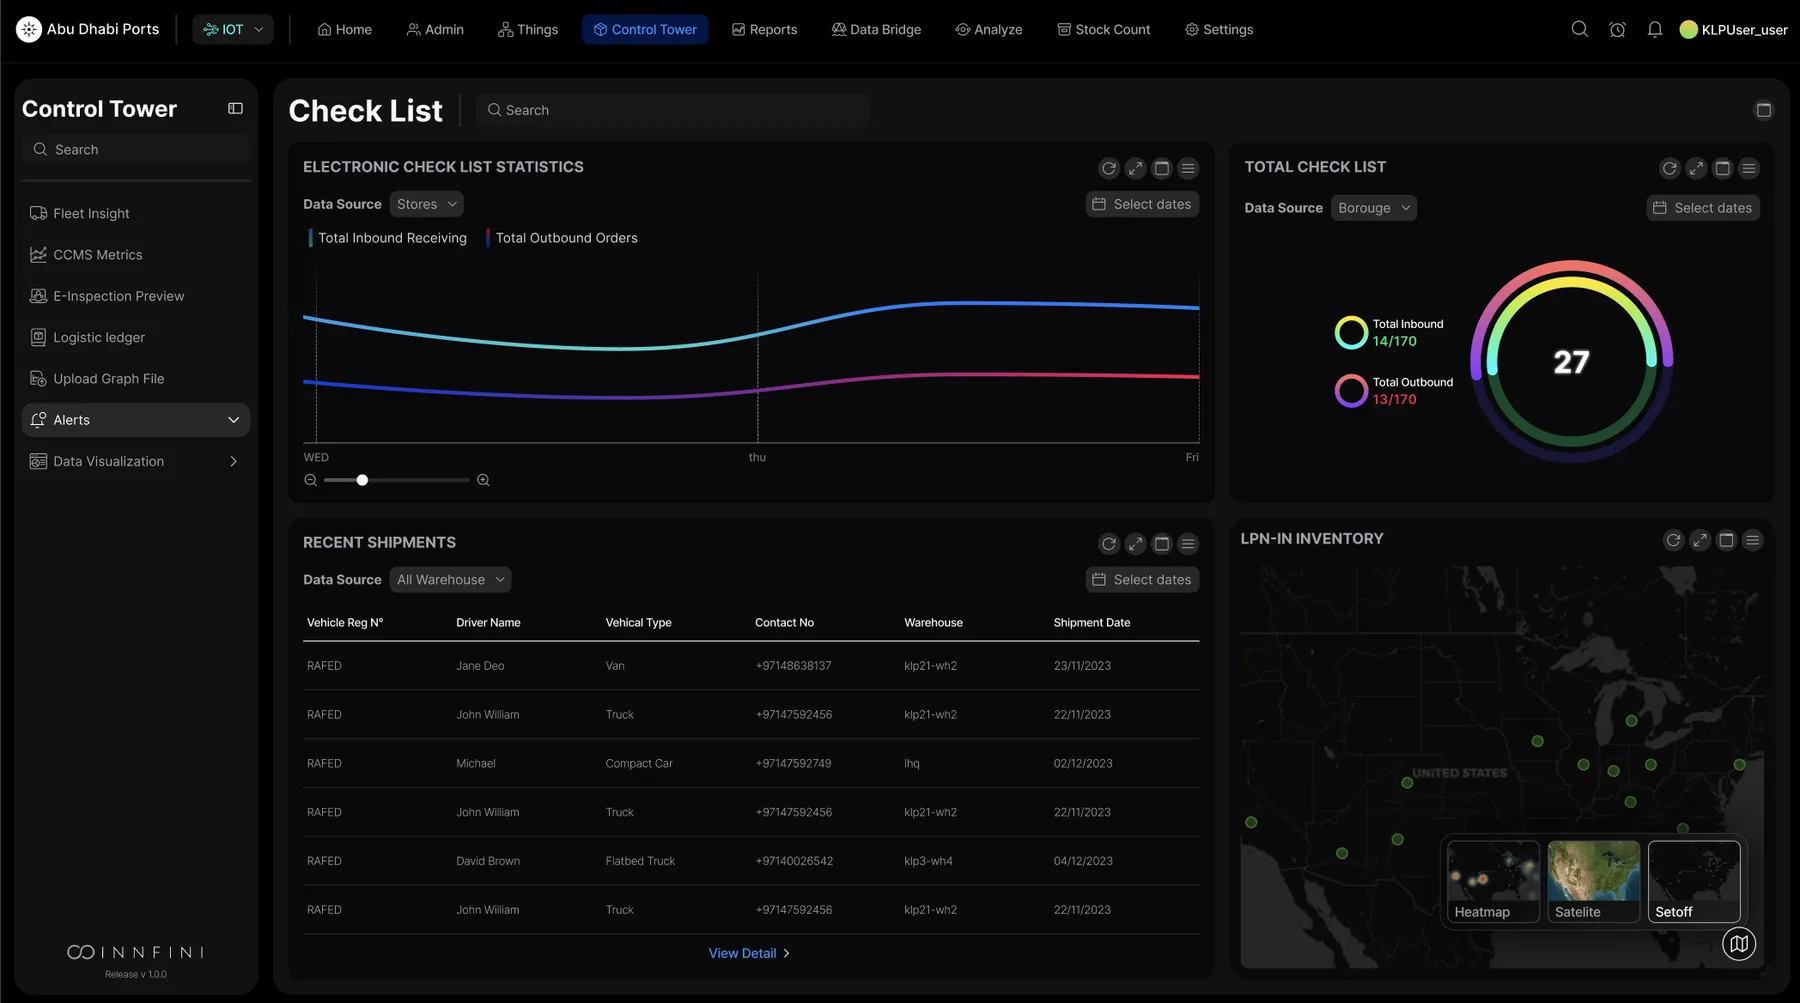
Mapped to the standards that matter.
SOC 2 Type II
Annual independent audit. Continuous monitoring of security, availability, and confidentiality controls across the platform.
ISO/IEC 27001
Certified information-security management system across product, infrastructure, and operations.
FedRAMP Moderate
3PAO assessment underway. Government-cloud authorization for federal civilian agencies. Q3 2026 target.
NIST 800-53
Control mapping across access, audit, configuration, and incident response. Documented baseline for federal-grade deployments.
HIPAA
Health-system deployments operate under signed Business Associate Agreements with PHI safeguards and audit trails.
GDPR & CCPA
Regional data-residency controls. Right-to-access and right-to-delete workflows built into the platform.
CJIS
CJIS-ready posture for law-enforcement deployments. Used by Dubai Police force-wide.
21 CFR Part 11
Electronic signatures, audit trails and access controls compliant with FDA Part 11 for life-sciences customers.
How we build.
- 01Encryption everywhere. AES-256 at rest, TLS 1.3 in transit, mTLS between every internal service. Customer-managed encryption keys for private cloud and on-prem deployments.
- 02Identity and access. SSO via SAML / OIDC. SCIM provisioning. Role-based + attribute-based access control. Hardware-key MFA enforced for administrative actions.
- 03Audit and provenance. Every operator action, every agentic decision, every data access logged to a tamper-evident audit ledger. Decision rationale traceable end-to-end.
- 04Sovereign & air-gapped deployment. Innfini runs in air-gapped, restricted-network, and sovereign-cloud environments. Operates degraded; reconciles on reconnect.
- 05Vulnerability management. Continuous SAST/DAST/SCA. Quarterly third-party penetration testing. Coordinated disclosure program with researcher rewards.
- 06Incident response. 24/7 SOC, follow-the-sun rotation. Documented incident response runbooks. Customer notification within 24 hours of confirmed material incident.
What this site puts on your device.
Very little. innovent.io is a static marketing site: it runs no analytics, no advertising pixels and no tag manager. The only cookie it writes is the one that records the choice you make in the consent banner, so we do not ask you again on every page.
| Cookie | Type | Retention | Purpose |
|---|---|---|---|
| innv_consent | First party | 180 days | Stores which cookie categories you allowed, and when. Written only after you choose. Contains no identifier and nothing about you. |
Two categories are listed in the preference centre but are not in use today. They are there so that your decision is already recorded if we ever introduce them:
Analytics
Would count visits and show which pages get read. Nothing of this kind runs on the site at present, and nothing will load unless this category is allowed.
Marketing
Would measure campaigns and support advertising elsewhere. Also not in use, and also gated behind your consent.
Two third parties do receive a request when a page loads, because the site fetches resources from them: Google Fonts serves the typefaces, and unpkg serves the mapping library used by one visualisation on the home page. Neither sets a cookie, though both necessarily see the connecting IP address, as any host of a requested file does.
You can change your choice at any time using the cookie preferences link in the footer of every page, or by clearing this site's cookies in your browser. Withdrawing consent is exactly as easy as giving it. For any question about data we hold, write to info@innovent.io.
Security questionnaires and audit access.
Customer security teams can request our latest SOC 2 report, ISO 27001 certificate, penetration test summary, and security questionnaire responses under NDA.